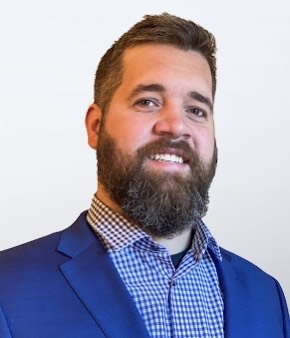
Hi, I'm Parker Brissette. I'm a cybersecurity leader based in Colorado, and everything on this site is my own independent work: researched, written, coded, tested, and fact-checked by me, on my own time. I built it because the security industry has a language problem. The acronyms multiply faster than anyone can learn them, and the people who most need this knowledge are often the ones the jargon locks out. Translating hard security ideas into plain English is the skill I have practiced my whole career, and this site is that skill turned into a public utility.
The conviction came from watching it matter. As CISO of Colorado's statewide court system, I briefed judges and administrators whose decisions depended on understanding risks that no one had ever explained to them without jargon. When security is explained plainly, people make better decisions; when it isn't, the jargon becomes its own vulnerability. I have carried that lesson through every boardroom since, and this site is where I practice it in public.
- 596 acronyms explained
- 259 framework controls translated
- 1,230+ practice questions
- 4 companion apps
- 100% free, no accounts
Try these first
AI Use Case Risk Tiering →
Govern a proposed AI use case in five minutes: answer eight questions, get a risk tier and the controls to match.
MITRE ATT&CK Adventure →
Play the attacker, the defender, or the developer, powered entirely by MITRE's official data.
Security Roadmap Planner →
Turn NIST CSF and CIS priorities into a tracked, sequenced plan.
What I bring to security
Leadership & strategy
Building security programs end to end: vision, roadmap, budget, team, and the board conversation. I translate cyber risk into business language, align spend with actual risk appetite, and lead organizations through the moments when it counts, including full ransomware recovery with zero business impact.
Governance, risk & compliance
Deep, hands-on fluency across NIST CSF, ISO/IEC 27001, SOC 2, PCI DSS, HIPAA, CIS Controls, GDPR, and SOX ITGC, from writing the first policy to sitting across from the auditor. The framework translations on this site come from years of making these standards make sense to real teams.
Security operations
Incident command, SOC leadership, detection engineering, threat modeling, and vulnerability management. I have built 24/7 operations from scratch, tuned detections to cut noise instead of adding to it, and I still write the queries myself.
Cloud & identity
Security architecture across AWS, Azure, and GCP, zero trust design, and identity and access management, from privileged access controls to OAuth flows. Cloud-first, least-privilege, and pragmatic about what lean teams can actually operate.
AI security & governance
Securing AI systems and governing their adoption: NIST AI RMF, OWASP Top 10 for LLMs, MITRE ATLAS, and ISO/IEC 42001, plus practical guardrails for model integrity, privacy, and prompt security. I also build agentic automation inside security operations, so the AI opinions here are earned, not borrowed.
Building & teaching
Everything in this ecosystem is hand-built, from this static, privacy-first TypeScript site to full-stack Next.js apps with real databases and auth, all automatically tested. Teaching is the through line of my career, and every quiz deck, metaphor, game, and assessment here exists to make someone better at this job.
The full menu
This glossary is the hub, but the kitchen doesn't stop there. Four companion apps, each built from the ground up:
MITRE ATT&CK Adventure →
A gamified security range built entirely from MITRE's official ATT&CK, D3FEND, and CWE/CAPEC data. Play the attacker across all 14 kill-chain phases, defend with 132 real countermeasures mapped to 418 techniques, or spot and fix real code weaknesses in secure-dev mode. Replay historical breaches, chase the daily challenge, and study catalogs that light up as you learn.
Business Impact Assessment →
A standards-based BIA platform grounded in ISO 22317, ISO 22301, NIST SP 800-34, and the BCI Good Practice Guidelines. Time-phased impact analysis derives MTPD, criticality tiers, and RTO/RPO gaps (never self-declared), then generates tabletop exercises from your own data and a complete, printable business continuity plan.
Lantern →
Shadow AI discovery for Microsoft 365. Connect a tenant once and Lantern inventories every AI app with a foothold: which OAuth grants it holds, who consented, who actually uses it, and what sensitive data reaches it. Eleven discovery lanes span consent grants, sign-in logs, Copilot audit activity, Purview DLP, Azure AI resources, SIEM queries, raw log files, and source code, each finding scored with plain-English recommendations.
Cyberdle →
The daily acronym game: guess it in six tries, and win or lose, walk away knowing what it stands for, why it matters, and where to read more. Practice and study modes drill the ones you miss, streaks keep you honest, and it installs as an offline-friendly app.
Latest writing
-
NERC CIP for Utilities, in Plain English
October 19, 2026NERC CIP for people arriving from IT: high, medium, and low impact, the ESP and PSP, the 35-day and 24-hour clocks, CIP-013, and what the RSAW really asks for.
-
OTP, HOTP, and TOTP: Which One Is Actually Protecting You
October 15, 2026SMS codes, counter-based HOTP, and time-based TOTP all answer to the name OTP. One barely counts, and none of them stops a phishing kit. Here is the ranking.
-
LLMNR and NBT-NS Poisoning: Find It, Then Turn It Off
October 12, 2026Why LLMNR and NBT-NS poisoning still opens most Windows pentests, how to detect it on UDP 5355 and 137, the exact GPO names, and why SMB signing matters more.
Credentials
Why it's free
Because the barrier to entry in security should be curiosity, not cost. There are no accounts here, no tracking, and nothing you type ever leaves your browser. The source is public on GitHub. If this site helps you pass a cert, brief your board, or finally understand what your vendor is selling you, it did its job.
Say hello
I'm always glad to join podcasts, panels, and webinars about plain-English security, AI governance, and building in public.